Security lessons from downed e-commerce sites and hot freezers

Two recent high-profile cyberattacks in the grocery space offer insights to retailers across all verticals about protecting their enterprises.
Within the past week, Ahold Delhaize USA, the U.S. subsidiary of Dutch supermarket conglomerate Ahold Delhaize, and French grocers including Carrefour, Monoprix, Intermarche and Cooperative U were hit by cyberattacks that left inoperative e-commerce sites, spoiled food and damaged equipment in their wake.
A closer look at each incident uncovers some valuable lessons for retailers looking to help protect themselves against similar security mishaps.
Ahold Delhaize USA - All for one and one for all
A network security incident caused Ahold Delhaize USA to take its e-commerce sites for all its banners - Food Lion, The Giant Company, Giant Food, Hannaford, and Stop & Shop, offline as of Monday, Oct. 12 (The sites remained offline as of Friday, Oct. 16).
Since fall 2025, all five Ahold Delhaize USA sites have been running on the same proprietary e-commerce platform. Developed and managed by in-house technology teams, the platform serves as the foundation of Ahold Delhaize USA’s ecosystem, supporting e-commerce, digital engagement and personalized customer experiences for each brand.
[READ MORE: Ahold Delhaize USA rolls out digital platform across banners]
Benefits the company says it has obtained from the platform include improved site performance, simplified account management, personalized promotions, a more integrated online ordering and fulfillment experience, and enhanced capabilities in advertising and retail media. The platform also enables faster deployment of new features and efficiency of resources across its portfolio, according to Ahold Delhaize USA.
However, along with shared efficiencies come shared vulnerabilities and risks. If a bad actor obtains entry to the back end of any one banner, whether by phishing, misuse of legitimate credentials or good old-fashioned system hacking, they can quickly and easily penetrate the systems of all banners on the platform.
Multi-brand retailers with this type of architecture need to also establish a common security framework and a real-time unified view of each banner’s operations to help ensure that a breach in one does not worm its way undetected through all.
French grocers - Being smart about Internet of Things
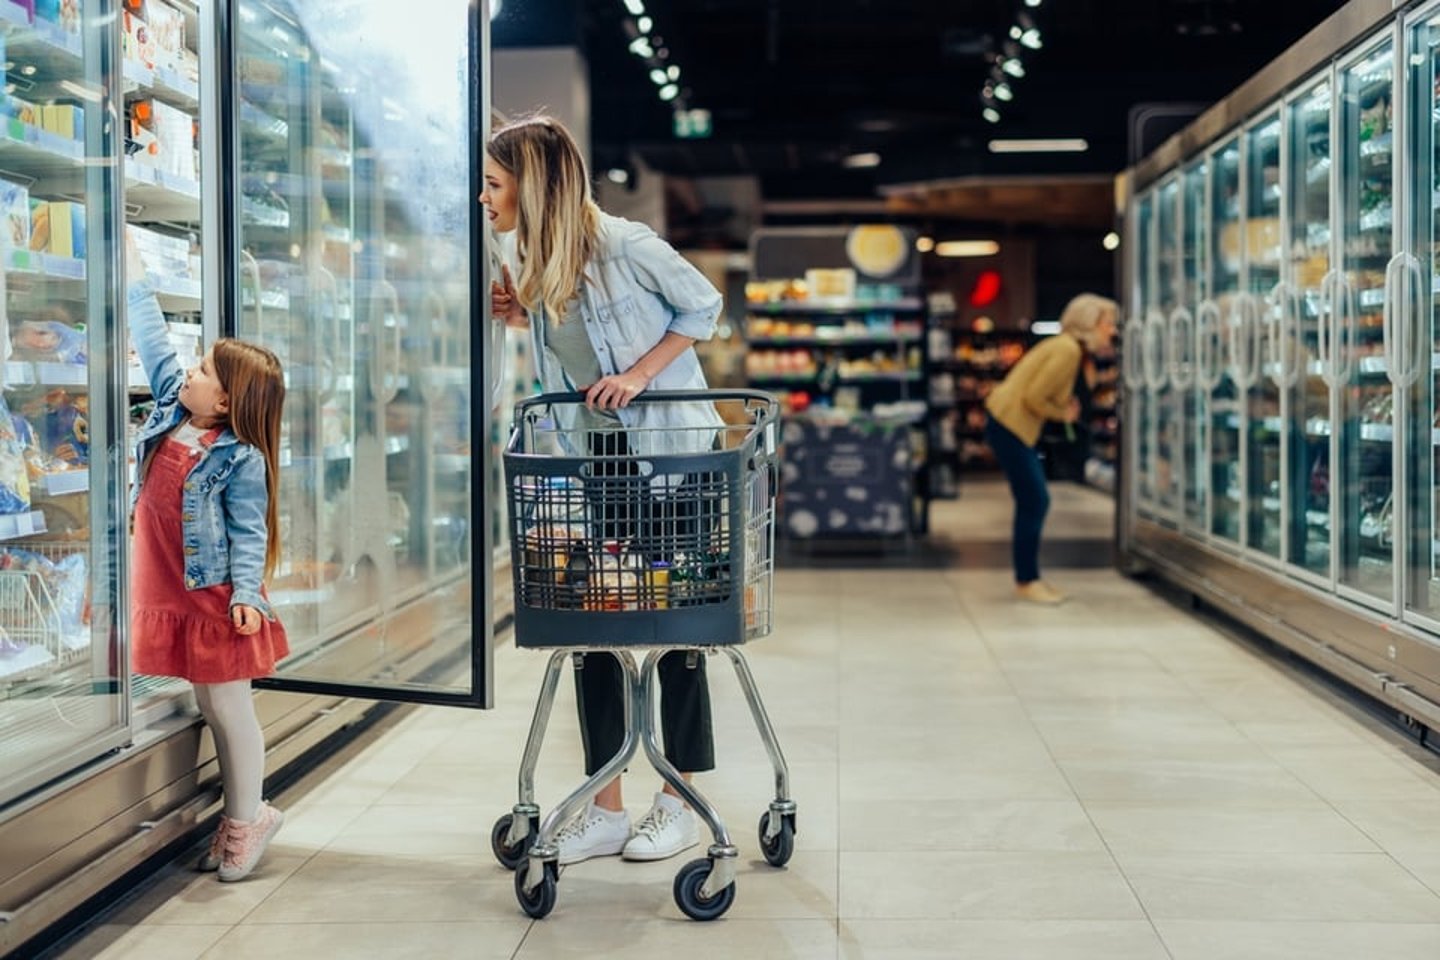
Monday, Oct. 12 also saw a cyberattack on roughly 350 supermarkets in France cause their freezers and refrigerators to heat up, and in some cases, catch fire, leading to millions of dollars in losses due to defrosted and perished food.
The Internet of Things, or IoT, connects hardware and physical infrastructure directly to the Internet. By making material objects “smart,” IoT enables them to be remotely managed and updated, operating more like software.
But IoT technology also opens physical infrastructure to the same type of hacking threats faced by digital software. For example, in the case of the cyberattack on grocery freezers in France, vulnerabilities in the firmware of the affected cooling systems allowed them to easily be accessed and manipulated by outside forces.
However, Danfoss, which provided the Internet-connected cooling systems which were hacked, has publicly said many of the affected units were at the end of their life and/or running outdated firmware, and that affected grocers had been warned to migrate and update outdated systems.
Retailers need to stay on top of their IoT infrastructure and make sure everything is up to date and not easily vulnerable to intrusion, In addition, they should take advantage of the ability of IoT sensors to monitor activity and send automatic exception alerts when an anomaly – such as a freezer heating to over 120 degrees Fahrenheit – occurs, enabling faster detection of potential breaches and the minimizing of resulting losses.